What Is A Hash In Crypto
A hash in crypto is a unique, fixed-size string of characters generated by a mathematical function that acts as a digital fingerprint for any piece of data, regardless of its size. This one-way cryptographic process ensures that even the smallest change in the input produces a completely different output, making it the foundational security mechanism for blockchain technology, transaction integrity, and cryptocurrency mining.
What is a hash in crypto?
At its core, a cryptographic hash is the output of a hash function, a mathematical algorithm that takes any input (a file, a transaction, a password, or an entire block of data) and produces a fixed-length string of characters, typically displayed in hexadecimal format. For example, the SHA-256 hash of the word "hello" is 2cf24dba5fb0a30e26e83b2ac5b9e29e1b161e5c1fa7425e73043362938b9824. Change one letter to "hellp," and the output becomes completely unrecognizable: 8c8a5c9c77e8b1e6c8c8c8c8c8c8c8c8c8c8c8c8c8c8c8c8c8c8c8c8c8c8c8c8 (actual value differs). This dramatic change is called the avalanche effect.
Three properties make cryptographic hashes indispensable in crypto:
- Determinism: The same input will always produce the exact same hash output. This allows anyone to verify data integrity by recomputing the hash and comparing it to the original.
- Pre-image resistance: Given a hash value, it is computationally infeasible to reverse-engineer the original input. A hash is a one-way street, you can go from data to hash, but never from hash back to data.
- Avalanche effect: A single bit change in the input flips roughly half the bits in the output, making any tampering immediately detectable.
How hash functions create a digital fingerprint
The internal workings of hash algorithms involve complex mathematics, but the logical process follows a clear structure. First, the input data is pre-processed to ensure it meets the algorithm's format requirements, this often involves padding the data to a multiple of a fixed block size (e.g., 512 bits for SHA-256).
Next, the data is partitioned into fixed-size blocks. Each block then goes through a series of data transformations, bitwise operations, logical functions, and modular arithmetic, that scramble the data in a deterministic but chaotic way. As each block is processed, an intermediate hash value is computed and fed into the next block's transformation, creating a cascading effect where every piece of data influences the final output.
After all blocks are processed, the algorithm outputs a fixed-length hexadecimal string. For SHA-256, that's 64 hexadecimal characters (256 bits). The crucial point is that this process is one-way, there is no mathematical shortcut to invert it. The only way to find an input that produces a specific hash is to try inputs one by one, which becomes computationally impossible for strong algorithms.
The final property that makes hashes reliable is collision resistance: it must be astronomically unlikely for two different inputs to produce the same hash. While collisions theoretically exist (since infinite inputs map to finite outputs), finding one for a secure hash function like SHA-256 would require billions of years of computing power.
Why blockchain depends on hashing
Blockchain technology would not function without cryptographic hashes. They serve four critical roles:
Transaction verification: Every transaction on a blockchain is hashed. The hash acts as a unique identifier and ensures that the transaction data hasn't been altered. When a node receives a transaction, it recomputes the hash and checks it against the claimed value. If they match, the transaction is valid.
Block linking: Each block in a blockchain contains the hash of the previous block. This creates an unbreakable chain of custody, block 100 contains the hash of block 99, which contains the hash of block 98, and so on. This linking is what makes the blockchain tamper-evident.
Immutability guarantee: If an attacker tries to change a single transaction in block 50, the block's hash changes. Since block 51 contains that hash, block 51's hash also changes, and so on down the chain. To successfully tamper with historical data, an attacker would need to recompute every subsequent block's hash before the network adds new blocks, a computationally prohibitive task.
Prevention of double-spending: By linking transactions in a chronological, hash-secured chain, the blockchain ensures that once a transaction is recorded, it cannot be spent again. Any attempt to create a conflicting transaction would require altering the entire chain, which is practically impossible.
SHA-256: The hash securing Bitcoin
Bitcoin, the first cryptocurrency, uses the Secure Hash Algorithm 256-bit (SHA-256) as its core hashing function. SHA-256 produces a 256-bit (64-character hexadecimal) output and is a member of the SHA-2 family, designed by the National Security Agency (NSA) and published in 2001.
In Bitcoin, SHA-256 serves three primary functions:
- Transaction verification: Each transaction is hashed to create a unique identifier and verify its integrity.
- Block hashing: Each block header is hashed twice (SHA-256d) to create the block's hash, which is then embedded in the next block.
- Mining (Proof of Work): Miners compete to find a nonce (a random number) that, when combined with the block header and hashed, produces a hash below a target threshold. The difficulty lies in the fact that there is no way to predict which nonce will produce a valid hash, miners must brute-force through billions of possibilities, consuming massive computational power.
SHA-256's strength lies in its collision resistance (estimated at 2^128 operations to find a collision) and pre-image resistance (2^256 operations to reverse). No practical attack has been found against SHA-256, making it the gold standard for blockchain security.
Keccak-256: Ethereum's hashing algorithm
Ethereum, the second-largest cryptocurrency, uses a different hash function: Keccak-256. Keccak was the original submission that won the NIST SHA-3 competition, but Ethereum uses the original Keccak variant, which differs slightly from the finalized SHA-3 standard (specifically in padding rules). This distinction is crucial, a hash computed with Keccak-256 will not match SHA-3-256 for the same input.
Keccak-256 uses a sponge construction rather than the Merkle-Damgård structure used by SHA-256. This design allows for variable-length output and provides strong resistance against length-extension attacks. In Ethereum, Keccak-256 is used for:
- Address generation: An Ethereum address is derived by taking the last 20 bytes of the Keccak-256 hash of the public key. This creates a one-way link from public key to address, preventing key recovery from the address alone.
- Smart contract hashing: The bytecode of smart contracts is hashed to create a unique identifier and ensure code integrity upon deployment.
- Internal data verification: Keccak-256 is used in Merkle Patricia Tries (the data structure that stores Ethereum's state) to verify account balances, contract storage, and transaction data without needing to store the entire dataset.
The choice of Keccak-256 over SHA-256 was partly deliberate, using a different algorithm reduces the risk of a single point of failure if one hash function is compromised.
Hashing, passwords and digital signatures
Beyond blockchain, cryptographic hashes protect digital systems in several practical ways:
Password storage: When you create an account on a website, the server doesn't store your password, it stores the hash of your password. When you log in, the system hashes your input and compares it to the stored hash. If the hashes match, you're authenticated. This ensures that even if a database is breached, attackers only obtain hash values, not actual passwords. (Note: modern systems use specialized password hashing functions like bcrypt or argon2, which are deliberately slow to resist brute-force attacks.)
File integrity verification: When you download a file from the internet, the provider often publishes a hash (e.g., SHA-256 checksum). After downloading, you compute the hash of the file yourself. If it matches the published value, you know the file hasn't been corrupted or tampered with during transmission. This is how software distribution platforms verify that downloads are authentic.
Digital signatures: In public-key cryptography, a digital signature is created by first hashing a message, then encrypting that hash with the signer's private key. The recipient decrypts the signature using the signer's public key, obtains the hash, and recomputes the hash of the received message. If both hashes match, the message is authentic and hasn't been altered. This is far more efficient than encrypting the entire message.
Hashing vs encryption: one-way or reversible
Hashing and encryption are often confused, but they serve fundamentally different purposes. Here's a clear comparison:
| Property | Hashing | Encryption |
|---|---|---|
| Purpose | Data integrity and verification | Data confidentiality and secrecy |
| Reversibility | One-way (irreversible by design) | Two-way (reversible with the correct key) |
| Output | Fixed-size hash value (e.g., 256 bits) | Variable-size ciphertext (same length as plaintext + padding) |
| Key requirement | No key needed | Requires an encryption key (symmetric) or key pair (asymmetric) |
| Determinism | Same input always produces same hash | Same input with same key produces same ciphertext; different keys produce different ciphertext |
| Security focus | Collision resistance, pre-image resistance | Confidentiality, key secrecy |
| Common use cases | Password storage, file checksums, blockchain, digital signatures | Secure communication (HTTPS), file encryption, email encryption |
In simple terms: hashing answers "is this data unchanged?" while encryption answers "who is allowed to read this data?" A hash is a fingerprint, it proves identity but reveals nothing. Encryption is a locked box, it hides contents but can be opened with the right key.
This distinction is why blockchain uses hashing, not encryption, for its core operations. The blockchain is public, everyone can see all transactions. What hashing provides is a way to verify that those transactions haven't been altered, without hiding them from view.
Related concepts
If you're exploring how hashing fits into the broader crypto ecosystem, these related topics are worth understanding:
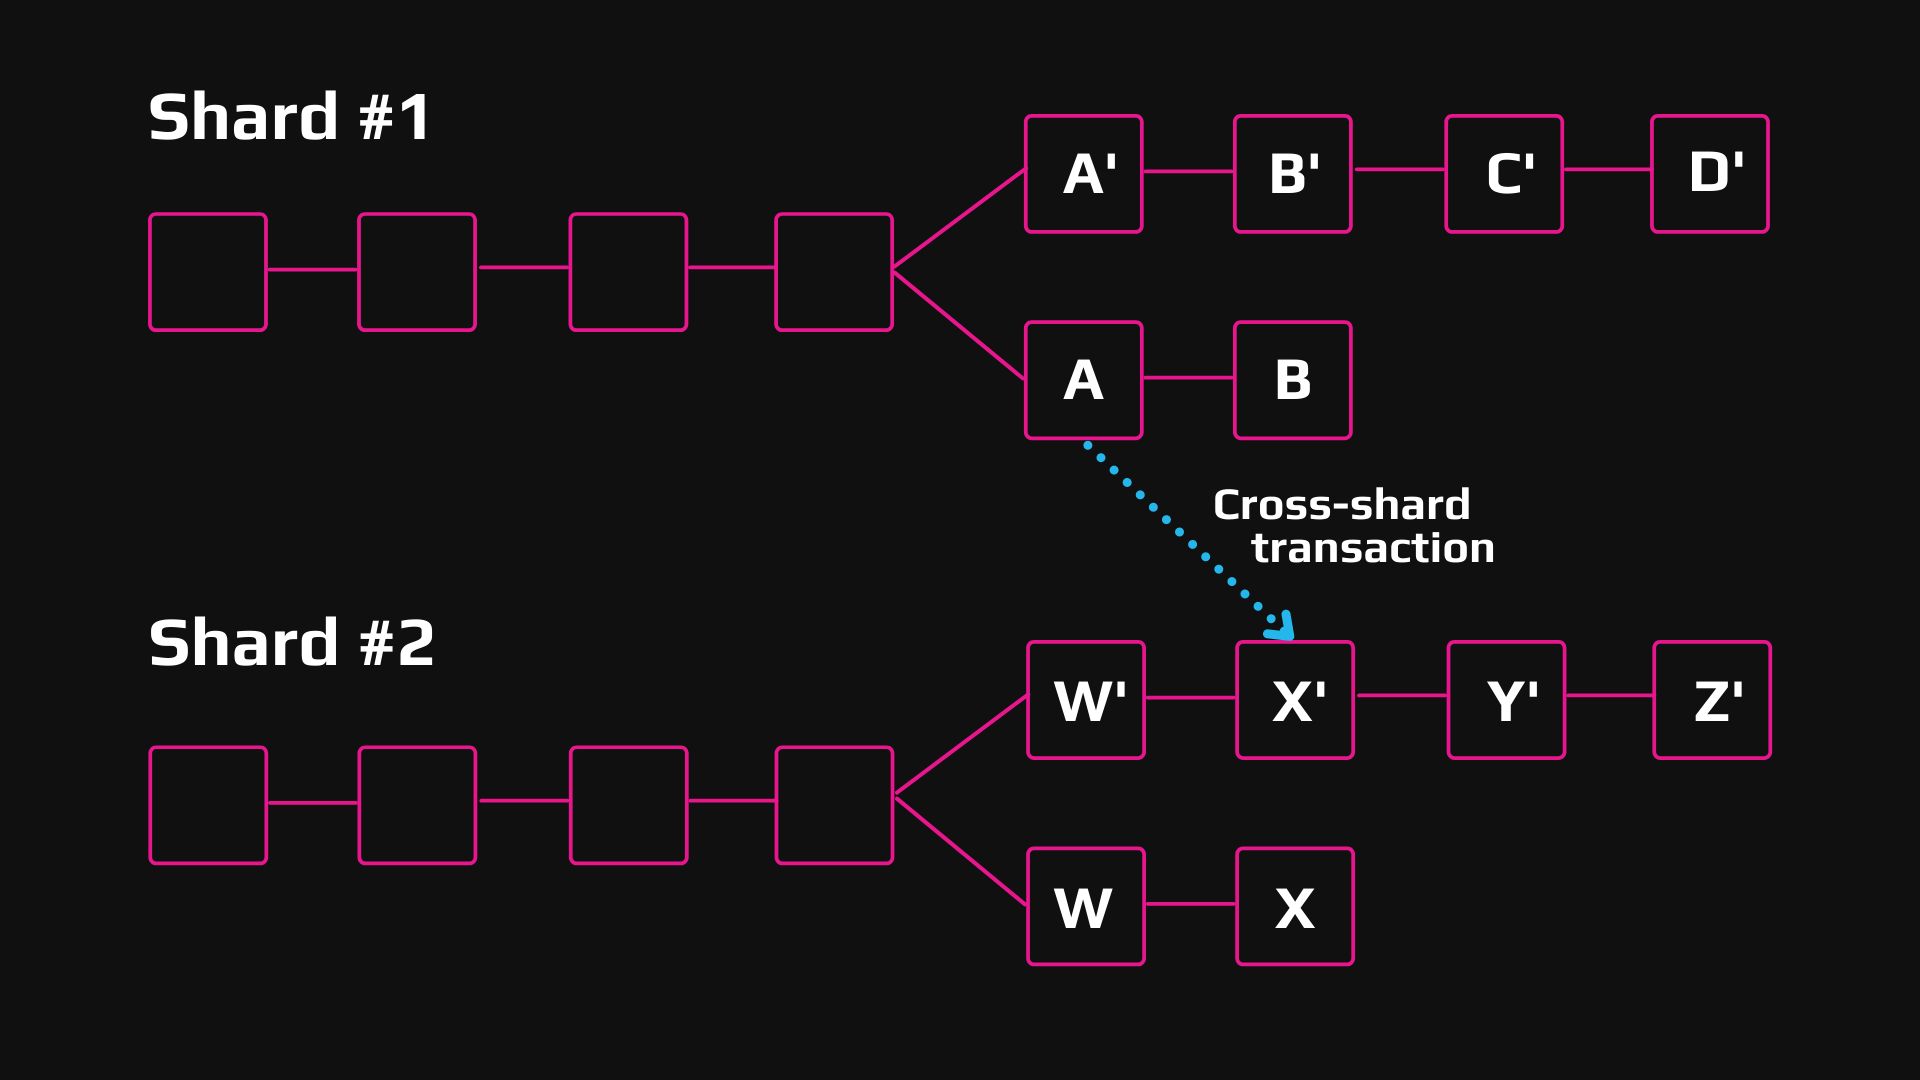
- What Is Sharding In Blockchain, Sharding splits a blockchain into smaller, parallel chains (shards) to improve scalability. Each shard maintains its own hash-based state, and cross-shard communication relies on hash commitments to verify data integrity.
- What Is Bridging In Crypto, Bridges transfer assets between different blockchains. They use hash-locking mechanisms and Merkle proofs (which are hash-based) to prove that a transaction occurred on one chain before minting tokens on another.
- How To Earn Interest On Crypto, Many DeFi platforms use hash-based smart contracts to automate interest payments and verify collateral positions. The security of your funds depends on the underlying hashing algorithms protecting the blockchain.
Understanding hashing is the key to understanding how cryptocurrencies achieve trust in a trustless environment. Every transaction, every block, every address, and every smart contract relies on the elegant simplicity of a one-way mathematical function that turns any data into a unique, verifiable fingerprint.