What Is An IP Range
An IP range is a contiguous block of Internet Protocol addresses grouped together for network organization, routing, and access control. Every IP address in a range shares the same network portion, while the host portion varies to identify individual devices within that network.
What is an IP Range?
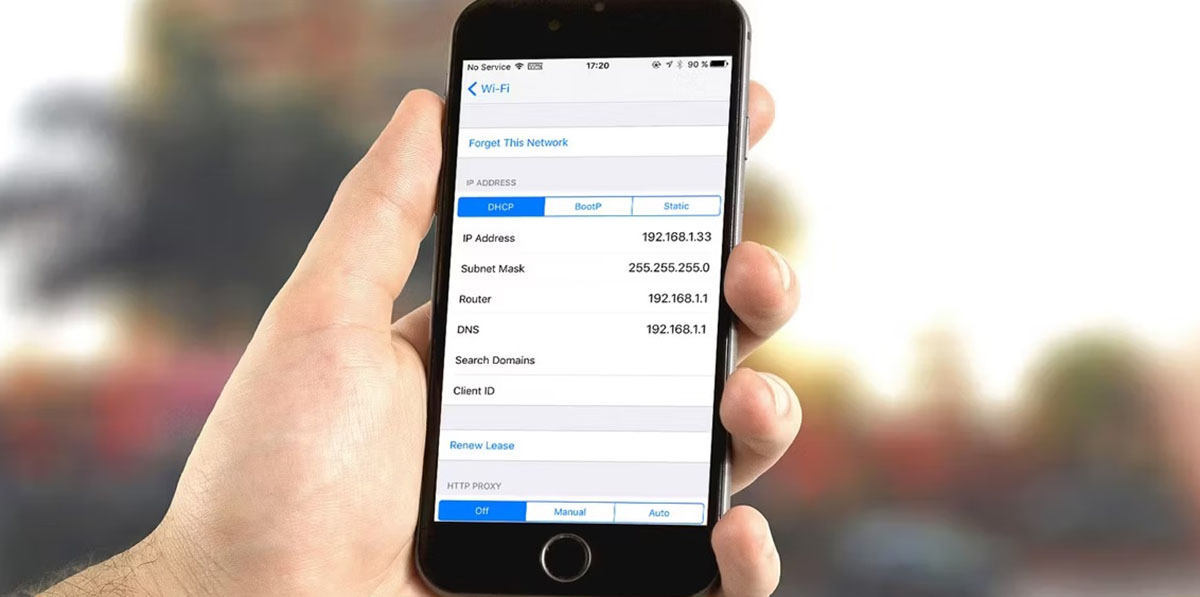
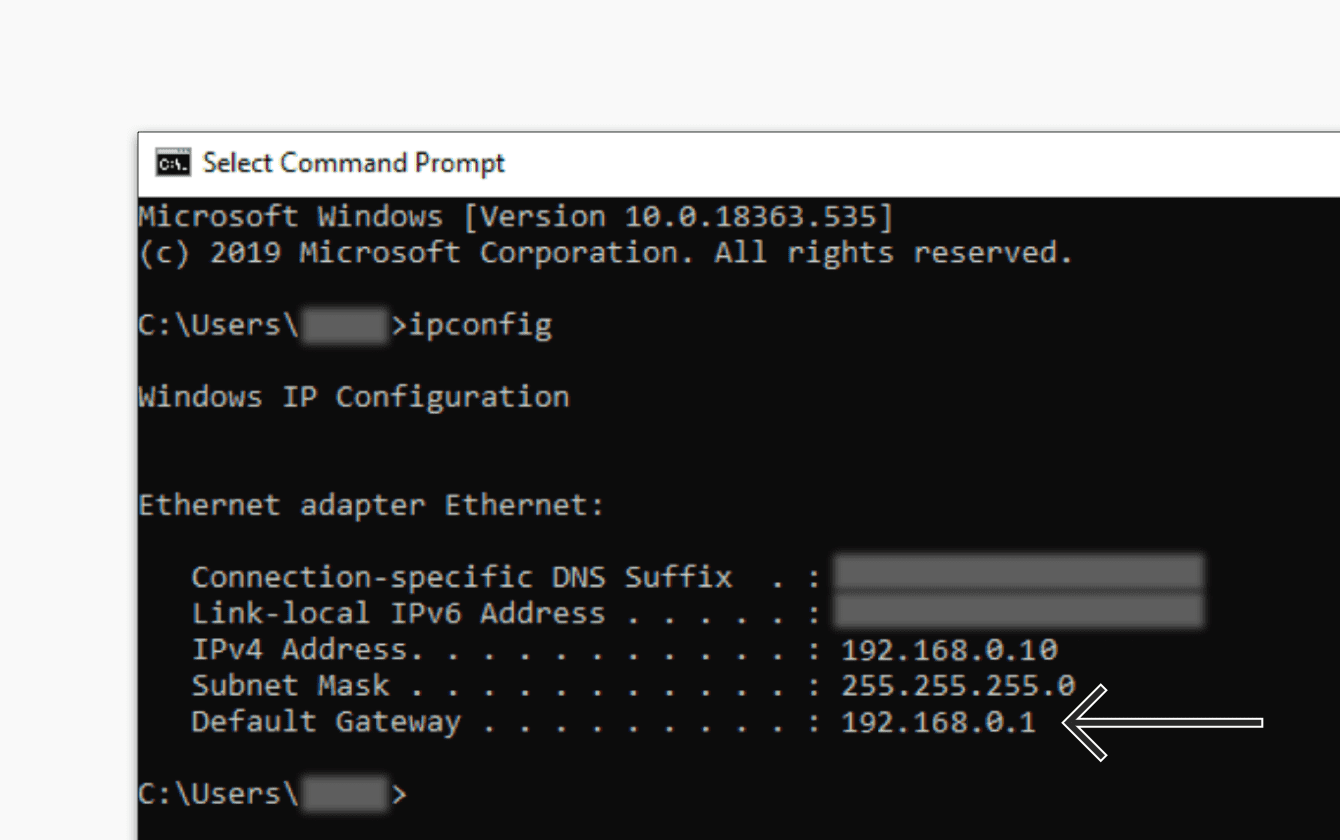
An IP range, also known as an IP address range, is a sequence of consecutive IP addresses that belong to the same network segment. Each IP address is a 32-bit number for IPv4, divided into four octets and written in dotted decimal format (e.g., 192.168.0.1). Within any IP range, every address consists of two distinct parts: a network portion, which identifies the group of devices, and a host portion, which identifies a specific device within that group. A subnet mask is used to separate these two portions, determining how many bits belong to the network and how many belong to the host.
For example, in the address 192.168.0.25 with a subnet mask of 255.255.255.0, the first three octets (192.168.0) represent the network, and the last octet (25) identifies the specific host. IP ranges are fundamental to routing, as routers use the network portion to forward data packets toward their destination, while the host portion ensures the packet reaches the exact device.
Private vs. Public IP Ranges
The most critical distinction in IP addressing is between public and private ranges. Public IP addresses are globally unique and routable on the public internet, allowing devices to communicate across the world. These addresses are assigned by Internet Service Providers (ISPs) from pools managed by regional registries under the authority of the Internet Assigned Numbers Authority (IANA).
Private IP addresses, in contrast, are taken from reserved blocks defined by RFC 1918 and are not routable on the public internet. They are designed for internal use within local networks, such as home LANs, corporate intranets, or cloud VPCs. The three primary private IPv4 ranges are:
- 10.0.0.0 to 10.255.255.255 (10/8 prefix), supports up to 16.7 million hosts, ideal for large organizations
- 172.16.0.0 to 172.31.255.255 (172.16/12 prefix), supports approximately 1 million hosts, suitable for medium-sized networks
- 192.168.0.0 to 192.168.255.255 (192.168/16 prefix), supports 65,534 hosts, commonly used in home and small office networks
Because private addresses are not internet-routable, devices using them must rely on Network Address Translation (NAT) to access public networks. This allows many devices to share a single public IP address, conserving the limited supply of public IPv4 addresses.
Understanding CIDR Notation
Classless Inter-Domain Routing (CIDR) notation is the modern standard for representing IP ranges concisely and flexibly. CIDR replaces the older classful system (Class A, B, C) that used fixed network boundaries, which led to significant address waste. With CIDR, an IP range is written as an IP address followed by a forward slash and a number, such as 192.168.1.0/24.
The number after the slash represents the network prefix length, the number of bits in the network portion of the address. For example, in 192.168.1.0/24, the first 24 bits (three octets) form the network portion, leaving the remaining 8 bits for host addresses.
CIDR notation also enables efficient subnetting. By extending the prefix length, you can divide a larger range into smaller subnets. For instance, a /24 range can be split into two /25 subnets, each accommodating up to 128 addresses. This flexibility allows network administrators to allocate addresses precisely according to need, minimizing waste and supporting hierarchical routing through route aggregation.
How to Calculate Addresses in a Range
Calculating the number of addresses in a CIDR block is essential for capacity planning and resource allocation. Follow these steps to determine both total and usable addresses:
- Identify the network prefix length: This is the number after the slash in CIDR notation (e.g., /24).
- Calculate host bits: Subtract the prefix length from 32 (the total bits in an IPv4 address). For /24, this gives 32 - 24 = 8 host bits.
- Compute total addresses: Raise 2 to the power of the host bits. For 8 host bits, 2^8 = 256 total addresses in the range.
- Account for reserved addresses: The first address in the range is the network address (identifying the subnet itself), and the last address is the broadcast address (used to send data to all hosts). Subtract these two from the total to get usable addresses: 256 - 2 = 254 usable host addresses.
- Apply for smaller subnets: If the range is further subdivided, repeat the calculation for each subnet individually, using the new prefix length for each division.
How to Define an IP Range
Defining an IP range for your network requires careful planning to ensure sufficient capacity, avoid conflicts, and support future growth. Follow this practical process:
- Identify the purpose: Determine what the range will serve, a department subnet, a VPN pool, a cloud VPC, or a guest Wi-Fi network. This defines the required number of hosts.
- Choose a CIDR block: Select a private IP range (e.g., 10.0.0.0/8, 172.16.0.0/12, or 192.168.0.0/16) and pick a subnet size that fits your host count.
- Calculate the subnet mask: Convert the prefix length to a subnet mask. This mask defines the network boundary.
- Define the range boundaries: The network address (first IP) and broadcast address (last IP) are determined by the subnet mask.
- Assign to devices or cloud networks: Configure the range on routers, firewalls, DHCP servers, or cloud VPCs. In cloud platforms, you specify the CIDR block when creating the virtual network, and the platform automatically handles routing and subnetting.
Always document your IP addressing scheme, including which ranges are assigned to which segments, to avoid overlaps and simplify troubleshooting.
IP Ranges in Cloud Networking
Cloud providers rely heavily on CIDR-based IP ranges to manage virtual networks. In Amazon Web Services (AWS), you define a Virtual Private Cloud (VPC) with a CIDR block (e.g., 10.0.0.0/16), then create subnets within that block for different tiers (e.g., 10.0.1.0/24 for web servers, 10.0.2.0/24 for databases). AWS publishes its current IP address ranges in a JSON file, listing all IPv4 and IPv6 prefixes in CIDR notation. This file enables administrators to identify traffic originating from AWS services and to configure security groups or network ACLs to allow or deny traffic to and from specific AWS service IPs.
Google Cloud uses a similar approach with VPC networks. Cloud administrators can reserve internal IP ranges and specify their usage type, FOR_SELF for ranges used only within the parent VPC, FOR_PEER for ranges used exclusively in peer networks, or NOT_SHARED for isolated ranges. By default, Google Cloud prevents you from reserving an internal range that overlaps with IP addresses already used by other resources in the same VPC, unless you explicitly enable overlap with subnets or routes. This safeguard prevents address conflicts and ensures clean network segmentation.
In both AWS and Google Cloud, internal ranges allow you to reserve blocks of private IP addresses for specific purposes, such as load balancers, Kubernetes pods, or managed services, while keeping them separate from the main subnet space. This granular control over CIDR ranges is essential for building scalable, secure, and well-organized cloud architectures.